Bring your team in securely with SSO
SAML or OIDC, tied to the identity provider you already use
Access, secrets and traceability handled where you deploy, not bolted on after
Trusted by +200 companies to simplify their infrastructure burden




The controls your security team expects, so you can run Qovery inside your own policies instead of around them.
SAML or OIDC, tied to the identity provider you already use
Scoped per project and environment, from read-only to full control
BYOC or BYOK, in your VPC or ours, Qovery runs wherever you need it
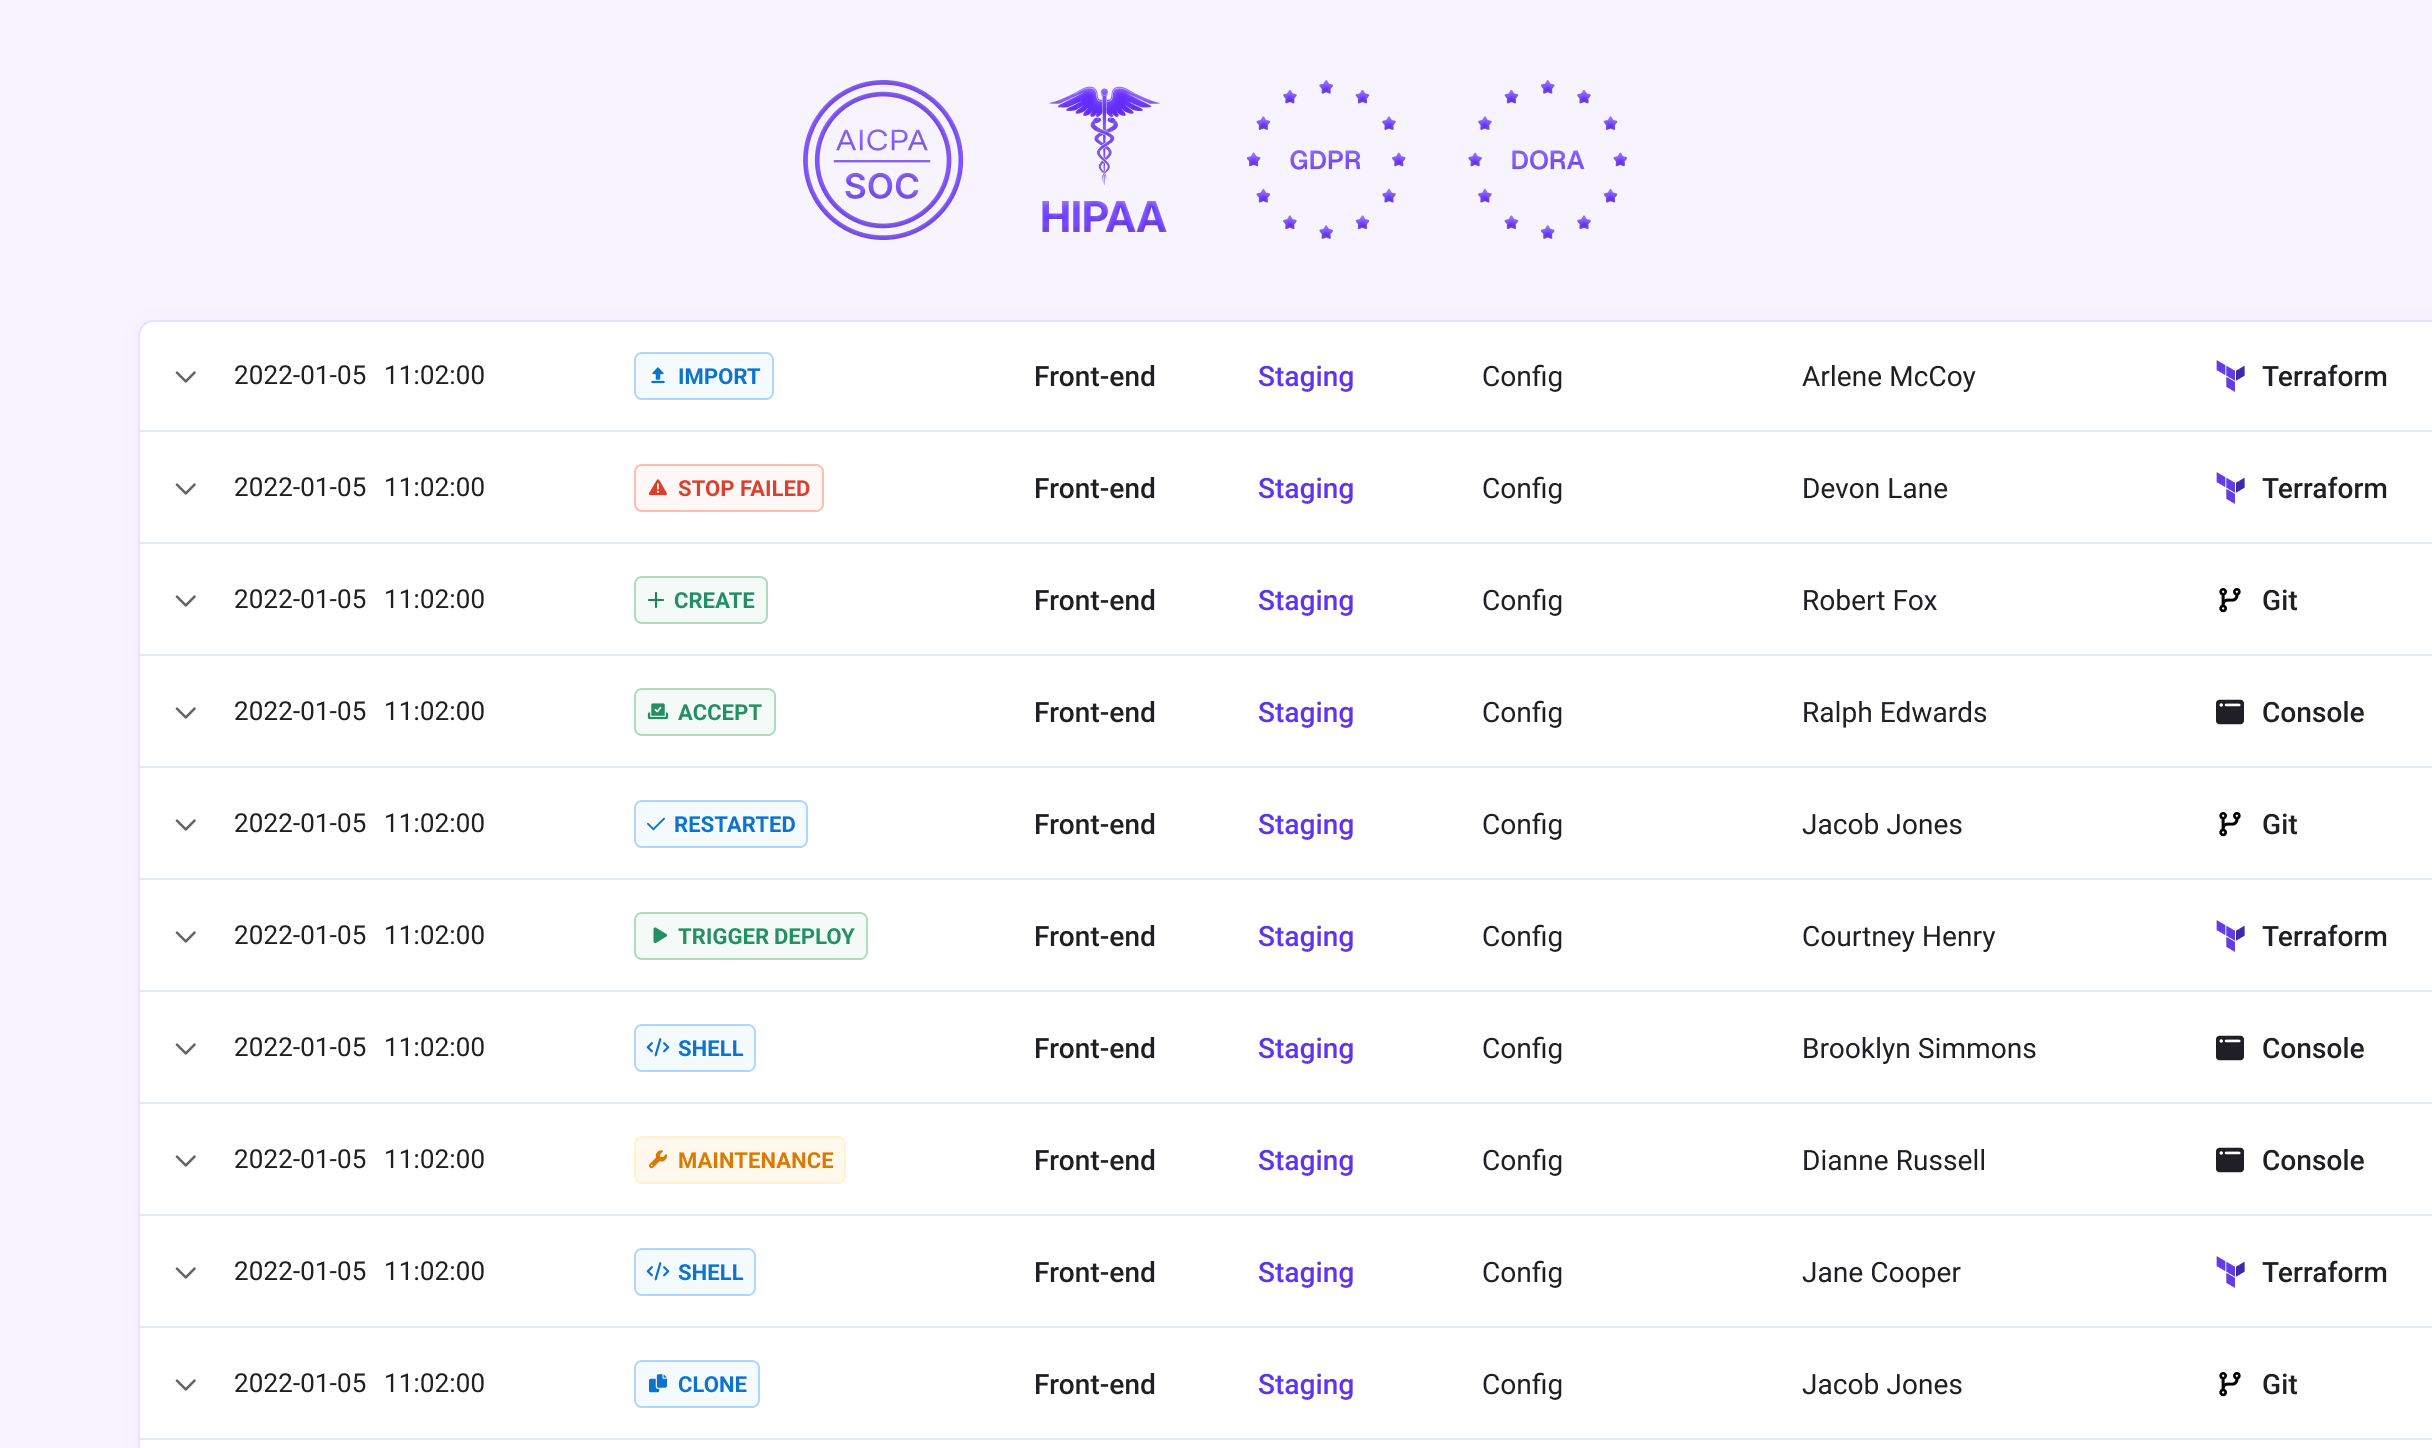
Attributed to each person and agent, with a minimum retention period of 365 days
Keep credentials in the vault you already use, not in Qovery
Every cluster Qovery provisions comes with encryption, network isolation, scoped IAM roles and a complete audit trail already in place. The controls auditors ask for are there before you need them, and our own certifications, including SOC 2 Type II, HIPAA, GDPR and DORA, back the platform underneath.
Trust center


From a compliance perspective, Qovery helps us see who has access to what, understand why someone is an admin, and review our infrastructure using agents and workflows pretty easily.
Gauthier Wallet
Founding Engineer at Lucis
The security settings your team needs, configured in Qovery instead of spread across tools
Define your own roles, with permissions per project and environment.
SAML or OIDC, mapped to the identity provider you already use.
Every action attributed to a person or an agent, with the retention you need.
Connect your existing vault instead of storing credentials in Qovery.
Run Qovery entirely inside your network, with no outbound connection to our infrastructure.
Deploy into your existing VPC and keep your own network rules.


 AIR-GAPPED